

A42 is updating AI SAST. You can now order it separately, without a subscription to the A42 Recon+Exposure platform, and scan code directly from GitHub.
AI SAST is an AI-powered static application security testing (SAST) tool developed by A42. It finds vulnerabilities before release, before the code reaches production and attackers can exploit them. AI SAST runs around 200 checks based on OWASP rules and A42’s own methodology, and supports most modern programming languages.
Every finding in the AI SAST report includes a severity level, a CVSS score, the vulnerability type according to the CWE classification, the file and line in the code, and steps to fix it. You can also download the report in Markdown format and pass it straight to an AI assistant to fix the code, or add it to your task tracker. A42 also lets your team manage findings until they are fully resolved: change the status of each finding, assign owners and track every action.
How AI SAST works: AI SAST
AI SAST Without the Platform Subscription
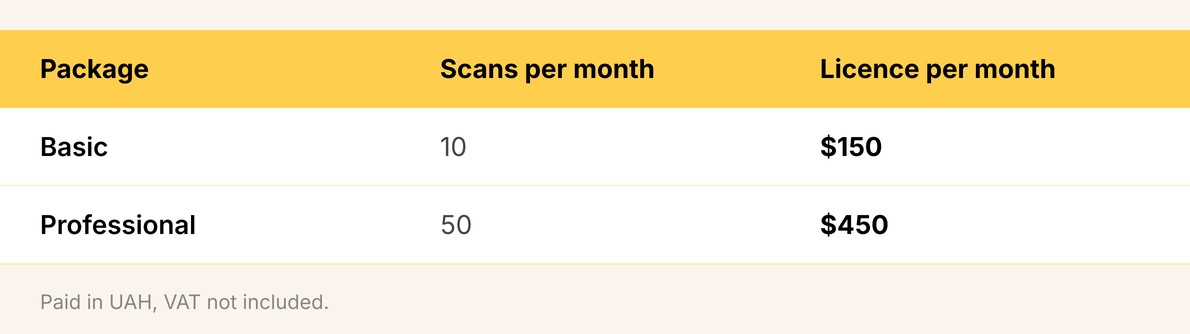
Until now, AI SAST was available only to A42 Recon+Exposure platform users. Teams that need code scanning without external perimeter monitoring can now order it as a separate service with a monthly licence. Nothing changes for platform users: AI SAST is still included in the A42 Recon+Exposure platform subscription at no extra cost.
AI SAST Pricing
 Scan GitHub Repositories with AI SAST
As before, you can upload code to the platform as a ZIP archive of up to 50 MB. A42 does not keep the archive, so you need to upload it again for each new scan.
You can now also scan code by connecting a GitHub repository. Just add the link, and AI SAST reads the code and starts the scan.
For a private repository, the scan runs inside GitHub Actions, the automated pipeline that builds your code. A42 generates a ready-made configuration file. Your team specifies the repository, the branch, and the folders to skip, then adds the file to GitHub. After that, AI SAST scans the code automatically on every push to the selected branch. This also works for repositories available only through a VPN, and for GitLab.
If AI SAST finds a vulnerability at the set level, the build stops and vulnerable code does not reach production. This makes security checks part of your DevSecOps pipeline. Your team chooses the threshold: Critical, High, or Medium. If you don’t need to stop the build, you can choose to receive reports only.
Order AI SAST Without a Platform Subscription
To get AI SAST, fill in the form.